Company profile
Bin Radan Cybersecurity
cybersecurity

Company services and solutions
Selected for larger ambitions
Specialist services for major business needs. Choose a solution and define the scope, location, duration and deliverables for a tailored technical and commercial proposal.
Group cybersecurity governance programme
- Order unit
- Enterprise programme
- Scope and specifications
- Policies, controls & improvement roadmap
Specifications and scope
Assess governance and risk across group companies and branches, then define policies, decision responsibilities and security investment priorities. Deliverables include a risk register, remediation roadmap and monitoring indicators reviewed with leadership and system owners.
A proposal is prepared after defining the service scope, location, duration and operating requirements. Deliverables and schedule are agreed before work begins.
Security operations centre programme
- Order unit
- Enterprise programme
- Scope and specifications
- Logs, alerts & response workflows
Specifications and scope
Design a security operations centre connecting system logs with detection cases, triage and incident escalation. Operating scope, coverage hours, team responsibilities and service targets are agreed after assessing environment size and available data sources.
A proposal is prepared after defining the service scope, location, duration and operating requirements. Deliverables and schedule are agreed before work begins.
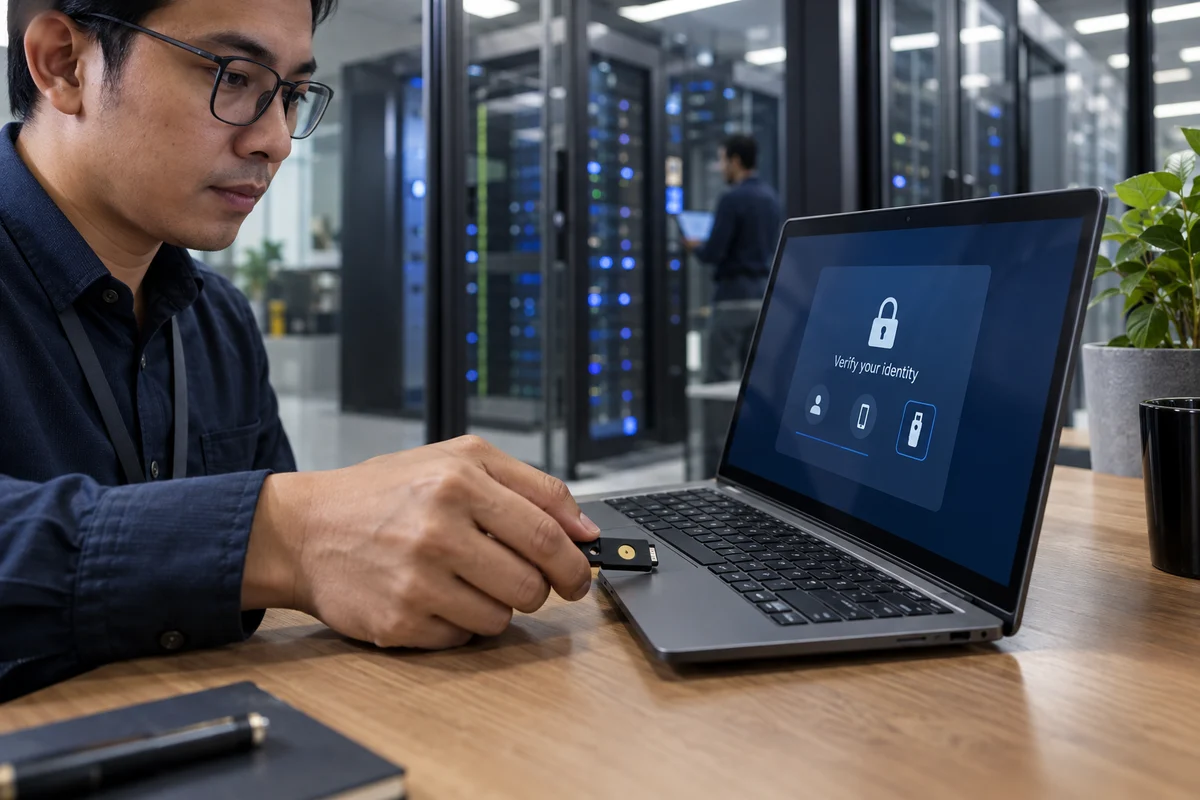
Cloud & enterprise identity protection
- Order unit
- Enterprise programme
- Scope and specifications
- Access, networks & data protection
Specifications and scope
Strengthen cloud environments and user identities through reviews of permissions, configurations, networks and sensitive data flows. The programme combines control design, implementation, validation and a documented change-management process.
A proposal is prepared after defining the service scope, location, duration and operating requirements. Deliverables and schedule are agreed before work begins.
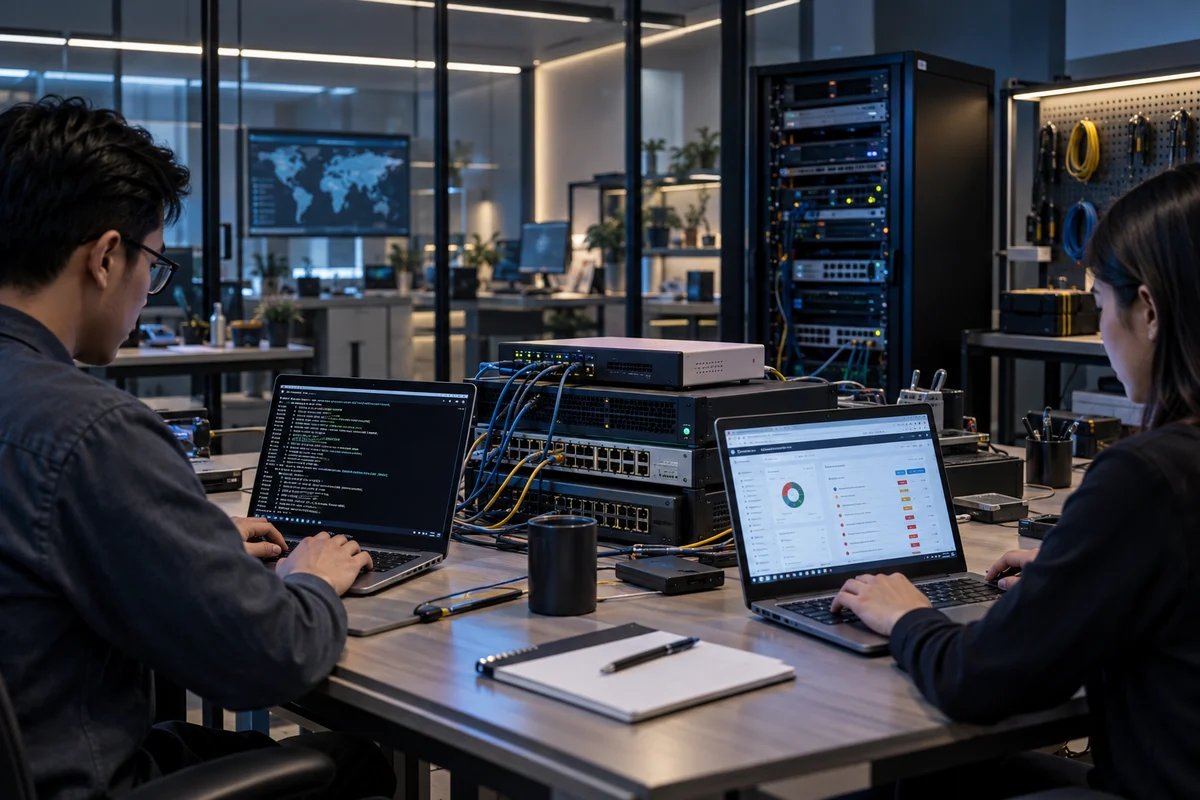
Enterprise security assessment programme
- Order unit
- Enterprise programme
- Scope and specifications
- Authorised scope, remediation & retesting
Specifications and scope
Assess agreed portals, applications and infrastructure under written authorisation, with findings prioritised by business impact. The programme includes remediation workshops, verification of addressed findings, and clear executive and technical reporting.
A proposal is prepared after defining the service scope, location, duration and operating requirements. Deliverables and schedule are agreed before work begins.
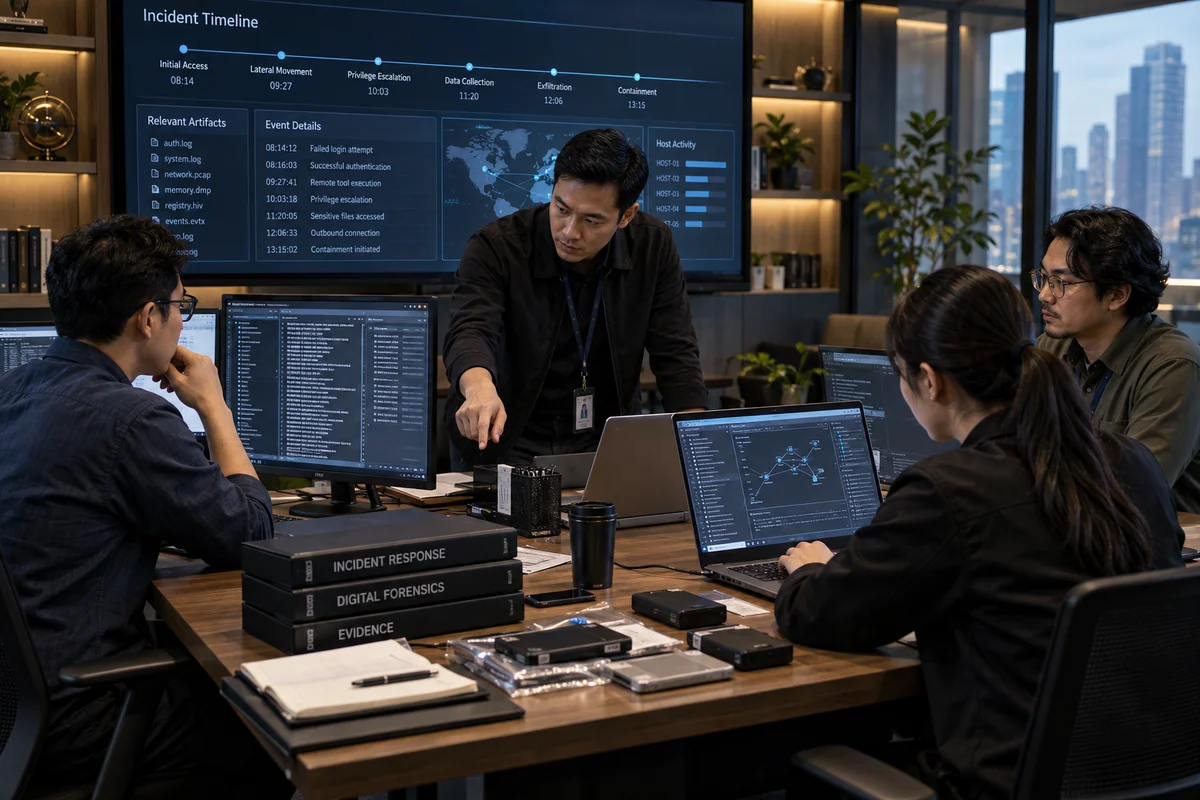
Cyber incident readiness & recovery
- Order unit
- Enterprise programme
- Scope and specifications
- Response plans & coordinated exercises
Specifications and scope
Prepare a response framework connecting technical teams, leadership and communications, with escalation scenarios, simulation exercises and recovery planning for critical systems. Responsibilities, restoration objectives and support boundaries are documented in an agreed engagement.
A proposal is prepared after defining the service scope, location, duration and operating requirements. Deliverables and schedule are agreed before work begins.
Multi-site cyber resilience programme
- Order unit
- Enterprise programme
- Scope and specifications
- Branches, suppliers & business continuity
Specifications and scope
Review branch protection, connectivity, common controls, supplier risks and business continuity paths. The programme combines targeted awareness, readiness checks and a phased improvement plan that accounts for differences between operational sites.
A proposal is prepared after defining the service scope, location, duration and operating requirements. Deliverables and schedule are agreed before work begins.
Requirements, teams, duration and deliverables are defined in a tailored proposal before work begins.
FEATURED VIDEO
Bin Radan Cybersecurity videos
Explore the company and its activities through its videos.
Watch the film on this platform · Video language: English
About the company
Bin Radan develops integrated cybersecurity programmes spanning governance, security monitoring, cloud protection, authorised assessments and incident readiness. Each programme is scoped around asset sensitivity, operational priorities and the permissions granted by system owners.
The company's activities cover Group cybersecurity governance programme, Security operations centre programme, Cloud & enterprise identity protection, Enterprise security assessment programme, Cyber incident readiness & recovery, and Multi-site cyber resilience programme.
Activities and services
Group cybersecurity governance programme
Assess governance and risk across group companies and branches, then define policies, decision responsibilities and security investment priorities. Deliverables include a risk register, remediation roadmap and monitoring indicators reviewed with leadership and system owners.
Security operations centre programme
Design a security operations centre connecting system logs with detection cases, triage and incident escalation. Operating scope, coverage hours, team responsibilities and service targets are agreed after assessing environment size and available data sources.
Cloud & enterprise identity protection
Strengthen cloud environments and user identities through reviews of permissions, configurations, networks and sensitive data flows. The programme combines control design, implementation, validation and a documented change-management process.
Enterprise security assessment programme
Assess agreed portals, applications and infrastructure under written authorisation, with findings prioritised by business impact. The programme includes remediation workshops, verification of addressed findings, and clear executive and technical reporting.
Cyber incident readiness & recovery
Prepare a response framework connecting technical teams, leadership and communications, with escalation scenarios, simulation exercises and recovery planning for critical systems. Responsibilities, restoration objectives and support boundaries are documented in an agreed engagement.
Multi-site cyber resilience programme
Review branch protection, connectivity, common controls, supplier risks and business continuity paths. The programme combines targeted awareness, readiness checks and a phased improvement plan that accounts for differences between operational sites.
Operating approach
- Identify assets, prioritise risks and establish the scope and required authorisation.
- Implement agreed controls and assessments with evidence and remediation tracking.
- Deliver an improvement plan, readiness exercises and follow-up under the service agreement.
Company value proposition
Security programmes that connect executive oversight, technical delivery and clear response responsibilities.